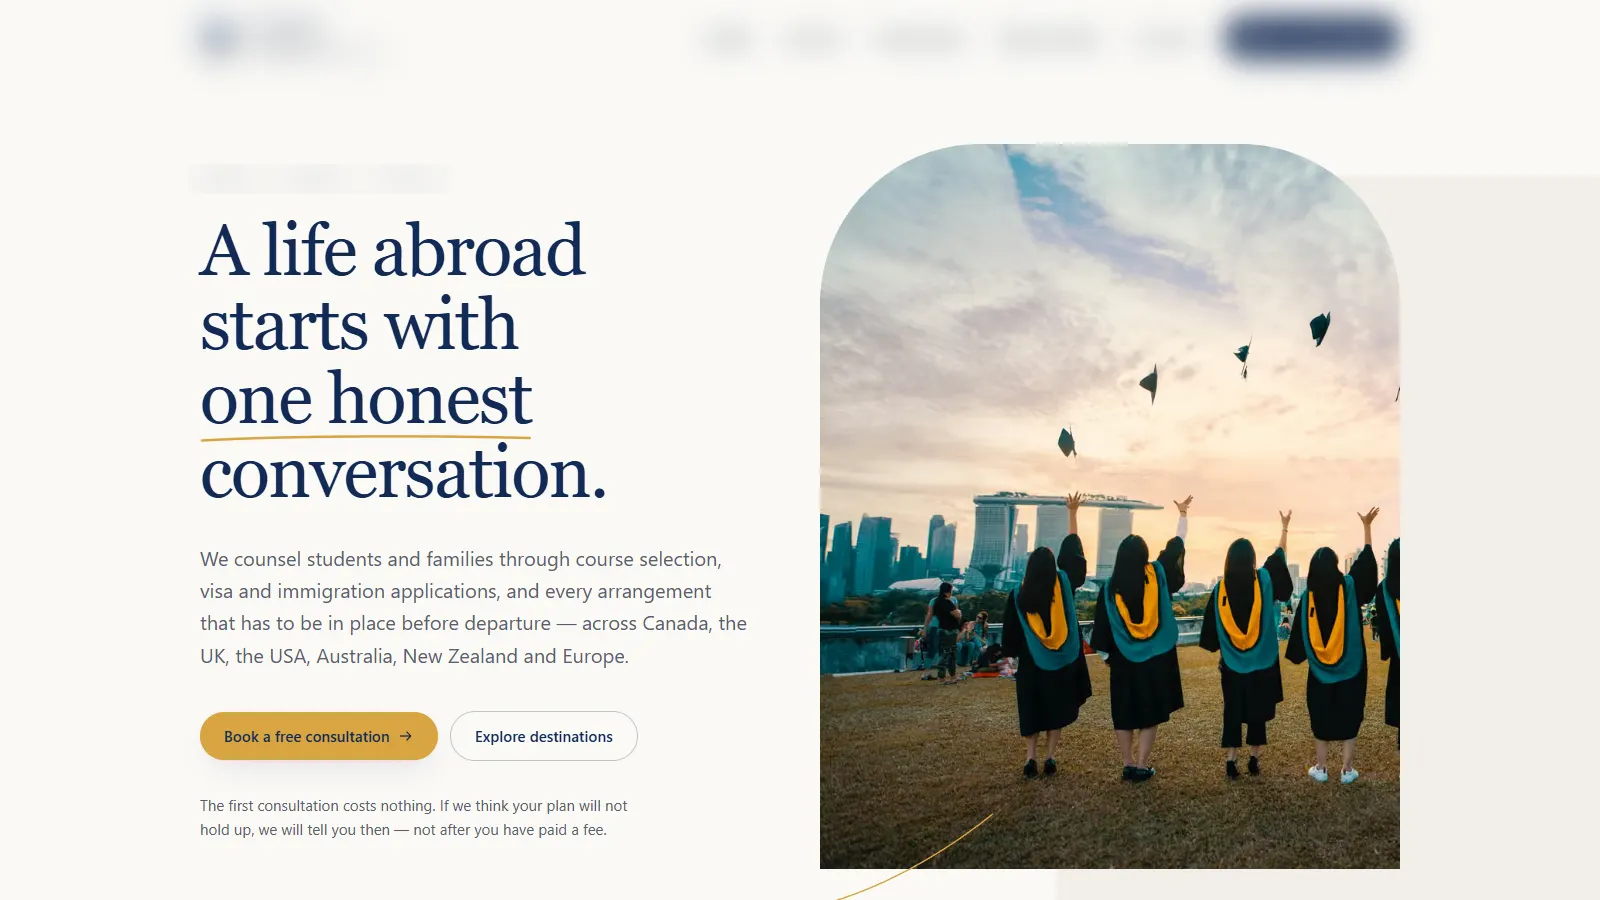
A marketing site for an Indian travel and overseas-education consultancy, with a focused admin panel where the client publishes student success stories. The panel was built, then audited against a running server, and every finding was fixed and re-tested before hand-over.
The Brief
The consultancy advises students and families on study abroad, visas and immigration, flights, test preparation and post-study career pathways, across six destinations. It needed a site that explains each destination and service clearly, and a way to add new success stories without waiting on a developer.
Two constraints shaped the build. Destination and service pages make regulated claims about visas and funds, so they belong in code review rather than behind a text box. And success stories feature named, photographed people on a page about immigration advice, so consent had to be enforced, not assumed.
What We Built
-
✦
A content-driven marketing site Destinations and services live as typed content arrays. Adding one object produces its index card, detail page, footer link, sitemap entry and contact-form option. Each destination page covers intakes, visa routes, funds requirements and post-study work rights.
-
✦
A success-stories admin The client signs in and creates, edits and publishes case studies, each with situation, challenge, approach and result sections that enforce a minimum length. Stories have draft and published states, a featured flag and manual ordering, and their destination and service are validated against the site's own lists.
-
✦
Consent as a hard gate A story cannot be published until written consent is confirmed. The form refuses, and the API enforces the rule again rather than trusting the form. Seeded placeholder stories carry a red "No consent" badge, so sample content stays visibly sample content.
-
✦
Portraits that survive redeploys The host wipes files written at runtime whenever it rebuilds, so uploads go to GridFS in the same database cluster. On upload, sharp corrects the EXIF rotation, crops to the 4:5 frame and converts to WebP, turning a 4 MB phone portrait into roughly 100 KB. Images are served with immutable caching and an ETag, and draft portraits stay private.
-
✦
Changes that show up immediately Every create, update and delete revalidates the homepage, the stories page and each destination page individually, so the client sees an edit at once instead of a stale cached page.
-
✦
Hardened after a live audit A probe script run against a live server found eleven issues, and each was reproduced before it was fixed. The login throttle had trusted a client-supplied forwarding header and allowed 40 straight password guesses. It now counts addresses from the trusted proxy side and also throttles per account. Admin API responses are now no-store behind the host's CDN, logout revokes the token on the server, a deleted account's session fails closed, oversize uploads are refused before the body is read, decoded image size is capped, and a CSP and full set of security headers ship in production.
The Stack
Next.js 16 on the App Router with React 19, TypeScript, Tailwind CSS 4 and Framer Motion. Data lives in MongoDB Atlas, with GridFS for images. Admin auth uses a single bcrypt-hashed account and a signed JWT in an HttpOnly cookie. Next 16's proxy gates the admin surface, and every route handler re-checks the session independently, because a guard that lives only in a route matcher fails open without anyone noticing. The marketing pages and the admin sit in separate route groups, so the admin carries none of the site chrome. Public reads return an empty list rather than throwing when the database is unreachable, which keeps both the live site and the production build standing. The app runs as a Node process on managed hosting, not as a static export.
The Outcome
After the fixes, a re-run of the audit found no open issues and all 93 functional checks passed. Those checks cover auth guards, validation, uploads, image caching, draft privacy, cascade deletes and cache revalidation, and npm audit reports zero vulnerabilities. The site was handed over with a plain-language admin guide written for the client, a deployment runbook covering the database, environment, seeding and host-specific gotchas, and a pre-launch checklist marking every placeholder that still needs real content.
Need something similar? Reach out — we build fast marketing sites with small, secure admin panels that clients can run themselves.